Security
Your customers trust you. We treat that seriously.
Plain answers about where your data lives, who can see it and what happens to it.
Stored in London
Your customer data is hosted in London, not scattered across regions.
Permissions that bite
Own, team or everyone: record access is enforced in the database, not just hidden on screen.
An audit trail
Role changes, exports, merges and key creation are all recorded.
Scoped API keys
Read-only or read-write keys that you can revoke in one click.
Erase on request
Download or permanently erase a person's data, and block their email from returning.
Your data stays yours
Export your data as CSV at any time (up to 50,000 rows per file), or, on Growth and above, schedule a regular copy to storage you own. Nothing is held hostage.
Permissions you can actually reason about
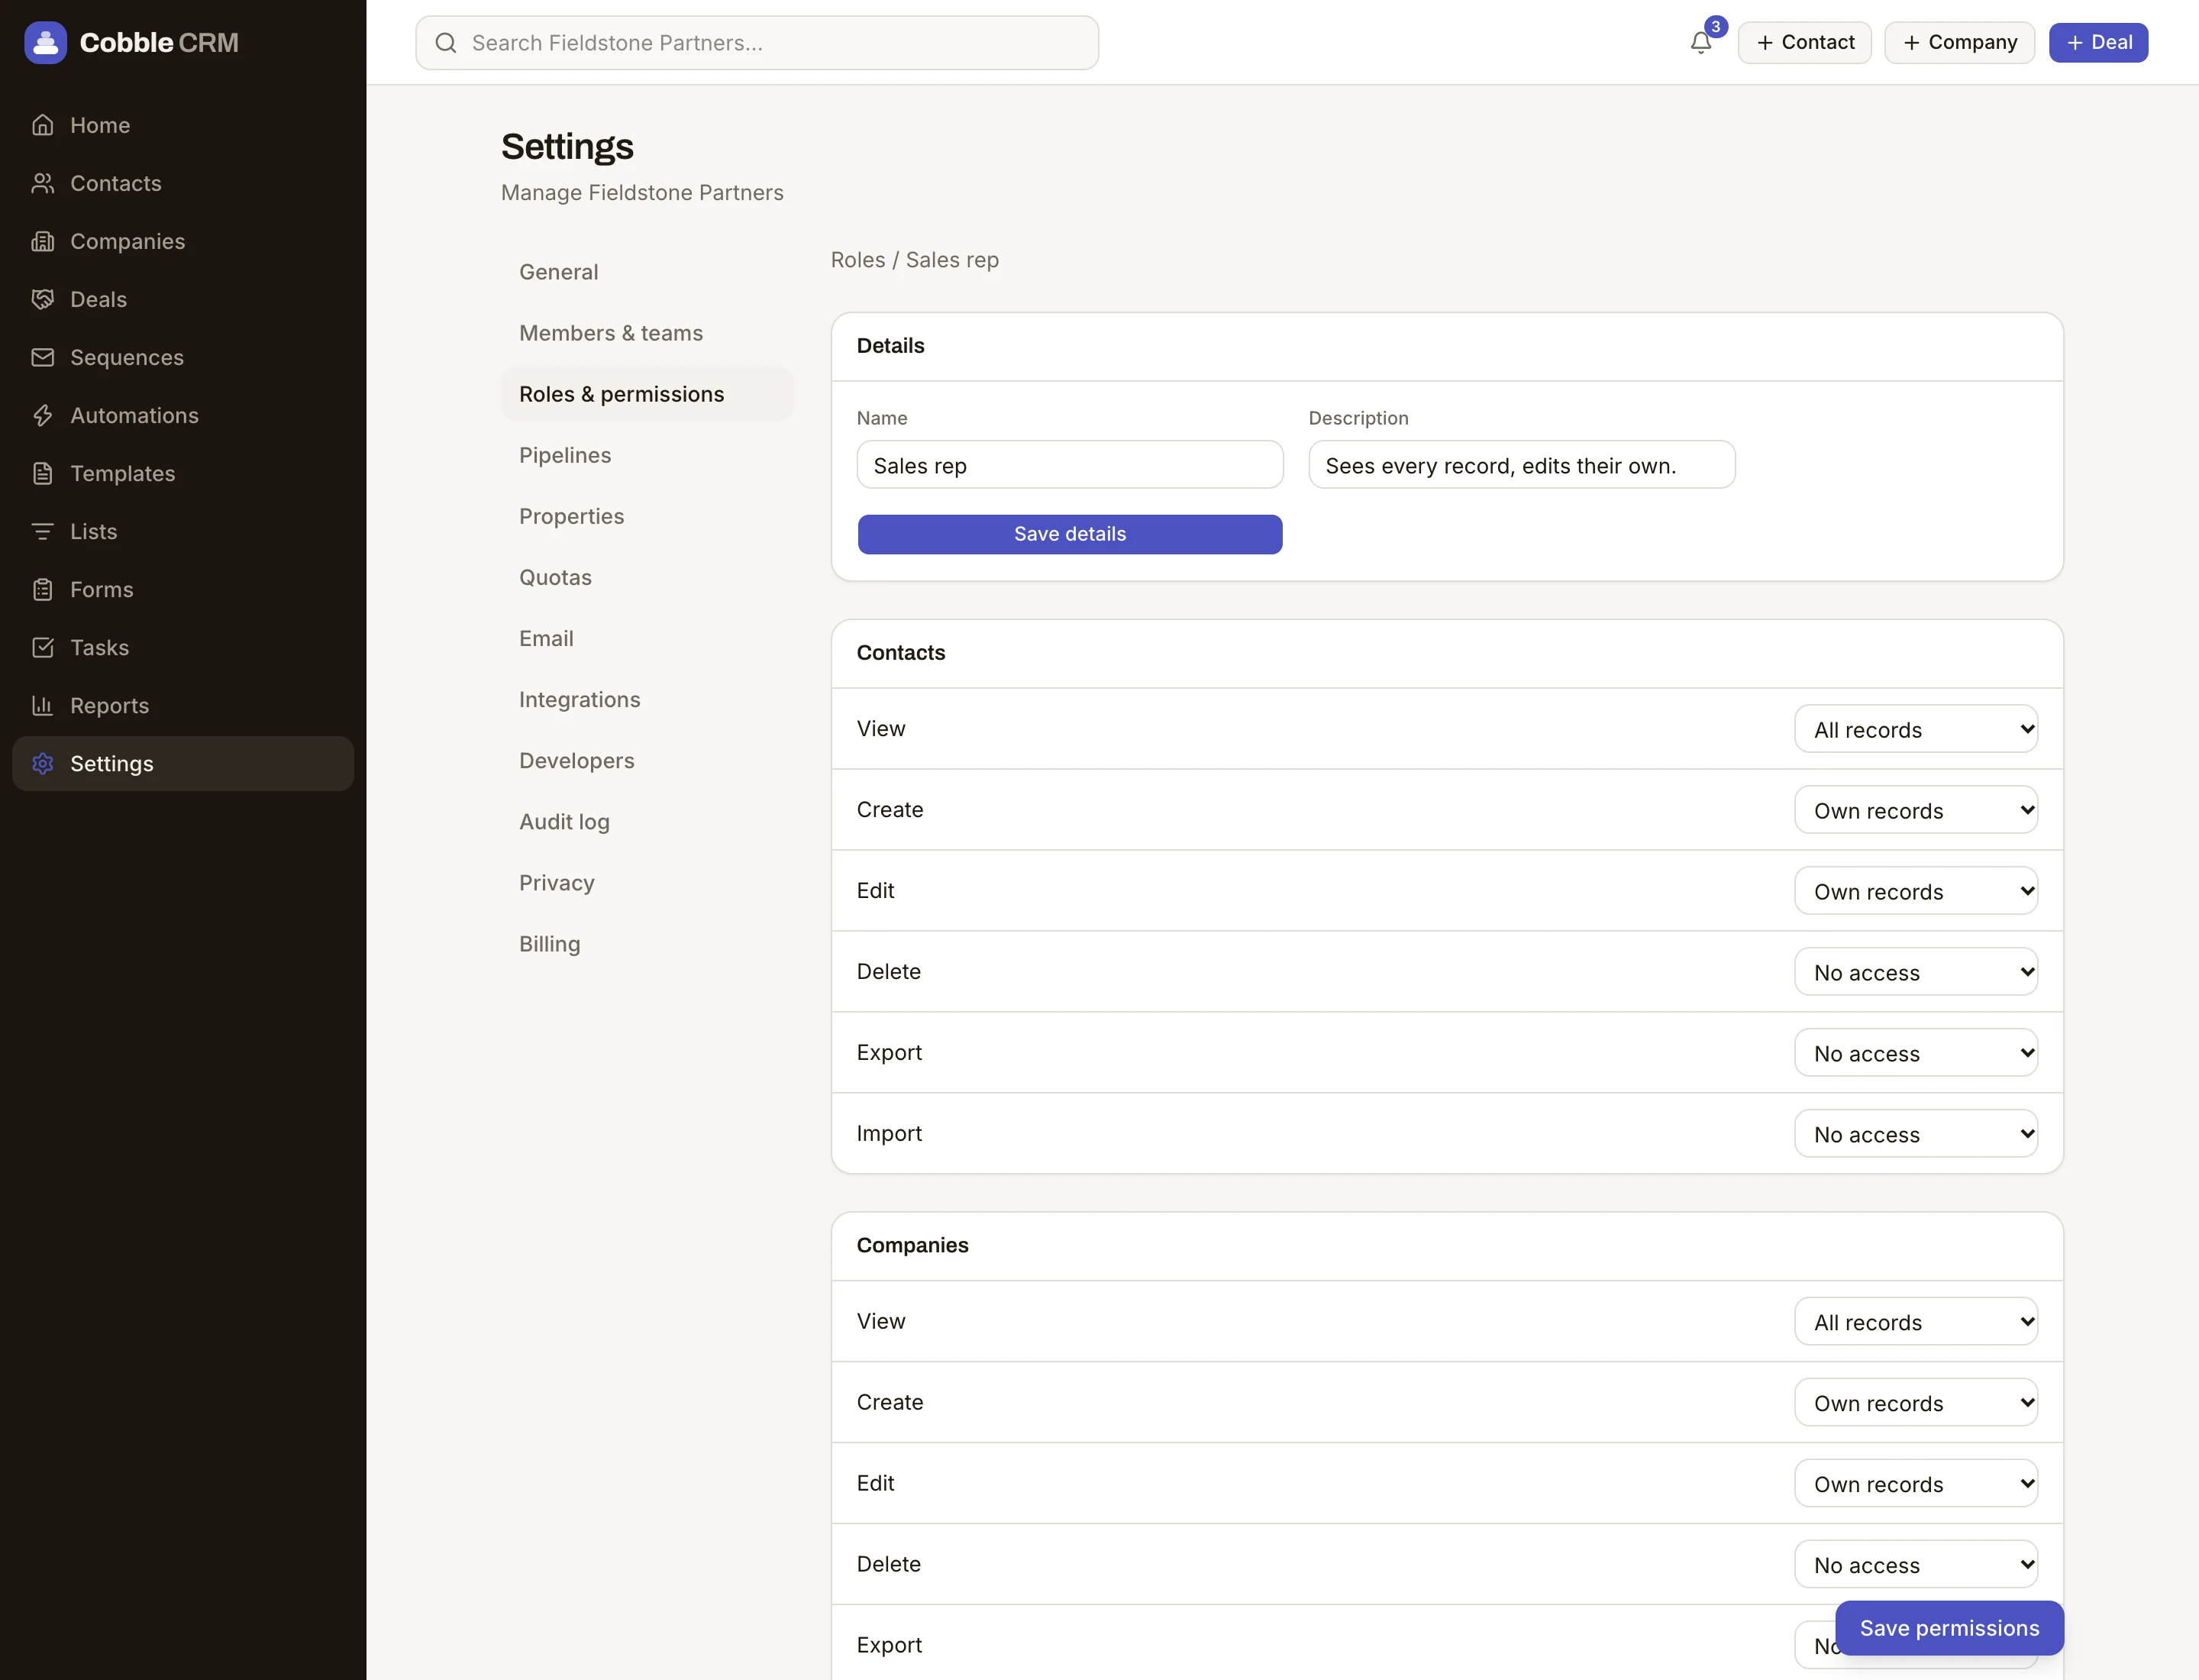
Build roles from a simple grid: for each kind of record, decide what a person can do and how far their access reaches. Everything below that is enforced in the database.
Per-object, per-action, own / team / all.
The detail
Isolated workspaces
Every record belongs to one workspace. For everything a signed-in person does, access rules in the database itself decide what they can see, so a bug in a screen can't show another company's records. Background jobs, the API and public forms are also limited to one workspace by the application.
Permissions by role
Roles grant access per object and action (view, create, edit, delete, export), scoped to your own records, your team's or everyone's. Reports and searches only ever count what a person can see.
An audit trail
Role changes, exports, merges, imports, API key creation and data erasure are recorded with who did them and when.
Scoped API keys
Create read-only or read-write keys, see when each was last used and revoke them instantly. Keys are stored hashed and shown only once.
Erase on request
Download everything held about a person, or permanently erase it and block their email address from being re-added.
Single sign-on (SAML)
Works with SAML 2.0 identity providers. Prove you own your email domain, then require single sign-on for the whole workspace. Available on Growth and above.
Multi-factor authentication
Sign in with an authenticator app, with recovery codes, and a workspace setting that requires it for everyone. Available on Growth and above.
Automatic user provisioning (SCIM)
Joiners, movers and leavers flow from your identity provider over SCIM 2.0. Deactivating someone blocks their access straight away and revokes their API keys. Works alongside single sign-on. Available on Growth and above.
Audit log export
Download the audit log, or stream it, signed, to your own security monitoring tool. Available on Growth and above.
Your data, on your schedule
Send a daily or weekly copy of your contacts, companies, deals and activities to an S3-compatible bucket you own (AWS S3, Cloudflare R2 or MinIO). Available on Growth and above.
Encryption in transit
All traffic to Cobble is over HTTPS. Mailbox connections use the providers' standard OAuth flows, so we never see your email password.
Subprocessors
Who handles your data
The companies that process customer data on our behalf. We will tell customers before we add or change one.
| Provider | What for | Location |
|---|---|---|
| Supabase | Database and sign-in | London, United Kingdom |
| Vercel | Application hosting | London (application servers); static pages via a global edge network |
| Stripe | Subscription billing | Per Stripe's published locations |
| Microsoft or Google | Email and calendar, only if you connect a mailbox | Per the provider |
Being straight with you
We don't yet hold third-party certifications such as ISO 27001 or SOC 2, and we won't imply otherwise. If your team needs to run a security review, send us your questionnaire at hello@cobblecrm.com and we'll answer it in writing, with architecture and data-flow detail.
Start free. Be selling in minutes.
Try Cobble with your real pipeline for 14 days. No credit card, no setup call, no pressure.